Claude Aids Cyberattacks , Cisco Flaws Exploited, CISA Adds Exploited
Quick Answer
This week’s cyber news highlights AI-driven attacks, exploited Cisco and GitLab flaws, ransomware breaches, phishing campaigns, and zero-days. Organizations should strengthen patching, identity security, and email authentication with SPF, DKIM, and DMARC.
This week’s cyber landscape was dominated by the growing role of AI in both attacks and defense, a wave of critical infrastructure vulnerabilities under active exploitation, and fresh breaches hitting fintech, government, and healthcare organizations. From Anthropic’s own threat intelligence report exposing state-sponsored abuse of Claude, to a maximum-severity Cisco firewall flaw being used to deploy ransomware, this week made clear that attackers are moving faster than ever — and that email and identity remain the weakest links.
Anthropic discloses state-sponsored hackers abusing Claude for cyberattacks
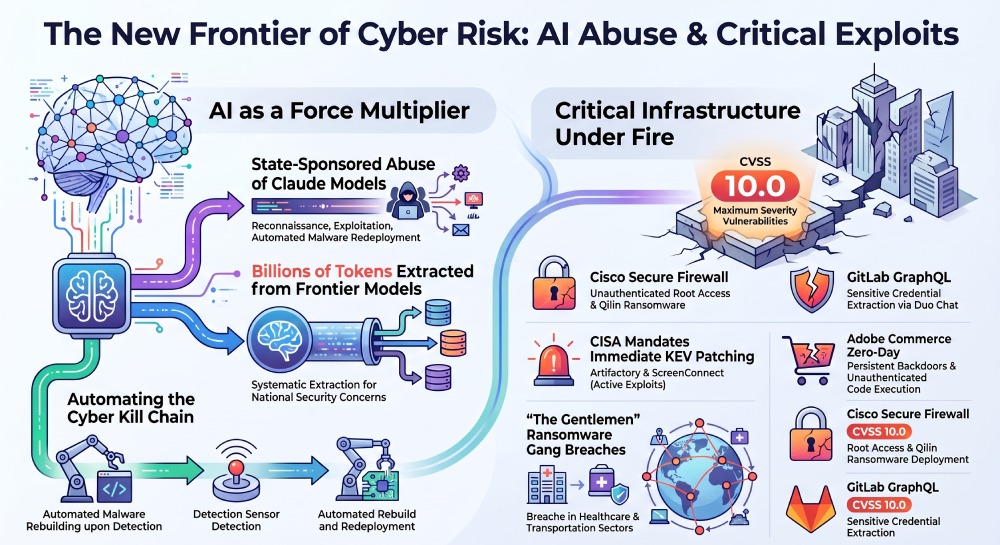
Anthropic published its September 2026 threat intelligence report, revealing that financially motivated criminals and state-sponsored espionage groups linked to Russia and China attempted to misuse its Claude models between December 2025 and August 2026. The report documents AI being used across the full cyber kill chain — reconnaissance, exploitation, and data theft — with one operation reportedly building tooling that could automatically rebuild and redeploy malware once detected by security products. Anthropic said no malicious activity was found on its Fable or Mythos models, which carry extra safeguards. https://thehackernews.com/2026/09/claude-used-to-automate-exploitation.html
Cisco firewall flaws exploited to deploy Qilin ransomware
Cisco confirmed that three separate threat clusters — a mix of state-sponsored and ransomware actors — exploited two previously patched Secure Firewall Management Center vulnerabilities to steal credentials and deploy Qilin ransomware. One of the flaws carries a maximum CVSS score of 10.0 and allows unauthenticated attackers to gain root access. https://thehackernews.com/2026/09/cisco-fmc-flaws-exploited-to-steal.html
CISA adds actively exploited Artifactory, ScreenConnect, and RouterOS flaws to its KEV list
CISA added five actively exploited vulnerabilities affecting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS to its Known Exploited Vulnerabilities catalog, giving federal agencies a strict remediation deadline. https://www.wiu.edu/cybersecuritycenter/cybernews.php
GitLab’s maximum-severity file-read flaw draws active exploitation attempts
A CVSS 10.0 GitLab vulnerability that lets an authenticated attacker with Duo Chat access extract sensitive credentials via a crafted GraphQL request is now being probed in the wild. CISA confirmed active exploitation and added it to its KEV catalog, giving federal agencies until September 14 to patch. https://thehackernews.com/2026/09/gitlab-cvss-10-file-read-flaw-draws-in.html
Dutch cybersecurity agency warns of imminent Check Point VPN exploitation
The Dutch National Cyber Security Centrum warned organizations of imminent exploitation of two critical Check Point VPN vulnerabilities, urging immediate patching before attackers weaponize them at scale. https://www.bleepingcomputer.com/news/security/
Microsoft warns of passkey phishing campaign hijacking cloud accounts
Microsoft disclosed two separate campaigns: one abusing third-party email delivery infrastructure to send over a million CEO-impersonation scam emails, and a second using passkey-themed social engineering to breach Microsoft cloud environments and exfiltrate data. https://www.wiu.edu/cybersecuritycenter/cybernews.php
Strengthening DMARC, DKIM, and SPF can help organizations reduce phishing, email spoofing, and identity-based attacks highlighted in this week’s cybersecurity news.
Veradigm confirms patient data breach tied to “Gentlemen” ransomware gang
Healthcare technology company Veradigm disclosed a data breach after a cybersecurity incident at a third-party vendor exposed patient personal data, with the attack claimed by the Gentlemen ransomware gang. https://www.bleepingcomputer.com/news/security/veradigm-discloses-patient-data-breach-after-gentlemen-gang-claims-attack/
“The Gentlemen” ransomware group also hits a Canadian airline
The same ransomware group behind the Veradigm breach claimed a separate attack on a Canadian airline this week, part of a broader pattern of the group targeting transportation and healthcare organizations across multiple countries. https://asec.ahnlab.com/en/95338/
LAPSUS$ resumes activity with “Chapter II,” teases new victim
The LAPSUS$ extortion group resurfaced this week with a new campaign chapter, teasing an upcoming victim disclosure, while a separate “AUDIT TEAM” extortion crew hit four organizations across South Korea, Germany, and Argentina. https://asec.ahnlab.com/en/95338/
Mathspace breach exposes data of more than 1 million students and parents
Online math learning platform Mathspace disclosed that attackers stole data belonging to more than a million students, staff, and parents after breaching its internal Metabase reporting system. https://www.privacyguides.org/news/2026/09/11/data-breach-roundup-sep-4-10-2026/
China-linked hackers exploit Tencent Sogou flaw to deploy GrayRabbit backdoor
Researchers found a China-aligned espionage group, tracked as UNC3569, exploiting a critical one-click remote code execution flaw in Tencent’s Sogou Input Method for Windows to deploy the GrayRabbit backdoor, primarily targeting government, education, and finance sectors in East and Southeast Asia. https://www.bleepingcomputer.com/
US says Chinese firms extracted billions of tokens from frontier AI models
A report this week detailed how Chinese firms have been systematically extracting billions of tokens’ worth of output from leading frontier AI models, raising fresh concerns about AI model theft and distillation as a national security issue. https://www.bleepingcomputer.com/news/security/us-says-chinese-firms-extracted-billions-of-tokens-from-frontier-ai-models/
Magento and Adobe Commerce zero-day used to backdoor online stores
Researchers at Sansec disclosed that attackers are exploiting an unpatched Magento and Adobe Commerce vulnerability to run unauthenticated server-side code and install persistent backdoors on e-commerce stores, with confirmed victims even among stores running Adobe’s latest security patches. https://thehackernews.com/2026/09/unpatched-magento-and-adobe-commerce.html
General Manager
Founder and General Manager of DuoCircle. Product strategy and commercial lead for DMARC Report's 2,000+ customer base.
LinkedIn Profile →Take control of your DMARC reports
Turn raw XML into actionable dashboards. Start free - no credit card required.