Binance Heist Record, Compromised DevOps Laptop, North Korean Attribution
Quick Answer
This cybersecurity news roundup covers major threats from October 27 to November 2, 2026, including the $6.3 billion Binance heist, North Korean cyberattacks, exploited zero-day vulnerabilities, malware campaigns, and critical security patches.
The cybersecurity landscape continues to evolve, with major threats targeting cryptocurrency platforms, enterprise systems, and critical infrastructure. This roundup covers key developments from October 27 to November 2, 2026, including the record Binance crypto theft, exploited zero-day vulnerabilities, emerging malware campaigns, and significant security patches. Discover the latest threats, attacker tactics, and essential security updates organizations should monitor.
Record $6.3 billion Binance crypto heist.
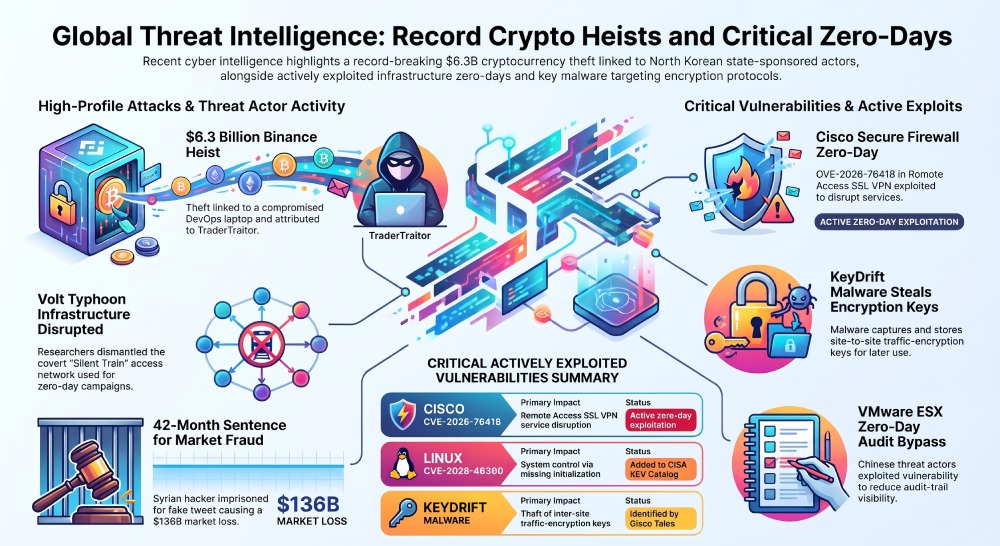
Binance lost roughly $6.3 billion in digital assets on 29 October, which is the largest crypto theft on record, about four times the Bybit hack of February 2025. Binance said it was investigating a potential security breach involving up to $5.8 billion in digital assets, and Tether said it had frozen more than $1.567 billion in USDT associated with the potential Binance hack. Source: https://bleepingcomputer.com/news/security/binance-probes-potential-58-billion-crypto-theft-hack Bleeping ComputerBleeping Computer
Binance traces the theft to a compromised DevOps laptop.
Binance later linked the $6.3 billion theft to a compromised DevOps laptop, according to BleepingComputer’s follow-up coverage from 30 October. Source: https://bleepingcomputer.com/news/security/binance-links-63-billion-crypto-theft-to-compromised-devops-laptop
Chainalysis and TRM point to North Korea’s TraderTraitor.
Blockchain analysts attributed the Binance theft to the North Korea-linked group. Chainalysis confirmed TRM Labs’ findings, stating with “a high degree of confidence” that TraderTraitor is responsible for the Binance $6.4 billion hack. Source: https://www.bleepingcomputer.com/news/security/binance-links-63-billion-crypto-theft-to-compromised-devops-laptop/amp/ Bleeping Computer
Cisco patches a Secure Firewall zero-day under active attack.
Cisco disclosed CVE-2026-76418 on 28 October. The flaw stems from logic errors in the Remote Access SSL VPN service when secondary authentication is configured on a tunnel group. Attackers can use it to force devices to reload and disrupt remote access. Source: https://cybersecuritynews.com/cisco-secure-firewall-0-day-vulnerability-exploited/ cybersecuritynews
CISA adds a Linux kernel flaw to its exploited list.
CISA added CVE-2026-46300, a Linux kernel missing-initialization bug that can help attackers gain control of affected systems, to its Known Exploited Vulnerabilities catalog on 28 October. Source: https://cybersecuritynews.com/linux-kernel-missing-initialization-vulnerability/
Weekly recap: Linux DDoS botnet, device-code phishing and Android spyware.
The Hacker News’s 2 November recap covers a range of threats, including a Linux DDoS botnet, device-code phishing, and Android spyware, alongside a long list of critical CVEs. Source: https://thehackernews.com/2026/11/weekly-recap-critical-cves-linux-ddos.html
Chrome, Firefox and other browser patches.
The same recap lists a batch of urgent fixes, including a Google Chrome flaw (CVE-2026-106378) and a range of Mozilla Firefox vulnerabilities, and urges users to patch those first. Source: https://thehackernews.com/2026/11/weekly-recap-critical-cves-linux-ddos.html
Chinese hackers exploit a VMware ESX zero-day.
A China-linked group exploited a VMware ESX zero-day to reduce audit-trail visibility, according to the week’s cybersecurity roundup, reported on 29 October. Source: https://www.wiu.edu/cybersecuritycenter/cybernews.php (I couldn’t reach the original vendor or researcher article, so this is an aggregator link.)
Volt Typhoon’s “Silent Train” access network.
Researchers linked the China-nexus group Volt Typhoon to a covert access network, dubbed Silent Train, that it used for zero-day exploitation campaigns. The network has since been disrupted. Source: https://www.wiu.edu/cybersecuritycenter/cybernews.php (aggregator link; original report not verified)
KeyDrift malware targets traffic-encryption keys.
Cisco Talos reported on 28 October on KeyDrift, malware designed to copy the keys that encrypt traffic between sites and store them for later use. Source: https://www.wiu.edu/cybersecuritycenter/cybernews.php (aggregator link; original report not verified)
Attackers probe a newly patched Oracle E-Business Suite flaw.
Threat actors began scanning for a critical Oracle E-Business Suite remote code execution flaw days after Oracle released a patch, according to threat intelligence firm Defused Cyber, reported on 28 October. Source: https://www.wiu.edu/cybersecuritycenter/cybernews.php (aggregator link; original report not verified)
Adobe fixes eight critical Campaign Classic flaws.
Adobe released patches for multiple critical flaws in Campaign Classic that could allow code execution, security feature bypass and privilege escalation. Source: https://www.wiu.edu/cybersecuritycenter/cybernews.php (aggregator link; original advisory not verified)
Syrian hacker sentenced over fake market-moving tweet.
A U.S. federal court sentenced Ahmad Umar Agha, a Syrian Electronic Army hacker known online as “Th3Pr0,” to 42 months in prison, according to a 30 October report. The fake tweet he posted triggered a $136 billion market drop. Source: https://www.wiu.edu/cybersecuritycenter/cybernews.php (aggregator link; court record not verified)
Organizations should strengthen email security with SPF, DKIM, and DMARC to help prevent phishing, spoofing, and unauthorized email use amid evolving cyber threats.
General Manager
General Manager of DuoCircle. Product strategy and commercial lead for DMARC Report's 2,000+ customer base.
LinkedIn Profile →Take control of your DMARC reports
Turn raw XML into actionable dashboards. Start free - no credit card required.